
Devenia / Learn / Technical SEO
Why a Site Still Says Not Secure After HTTPS
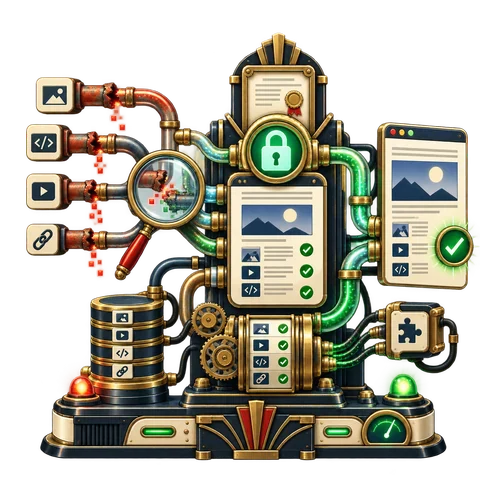
HTTPS is not complete until every resource is secure
You switched the site from HTTP to HTTPS, but the browser still shows a warning. First identify the cause: an invalid certificate, an HTTP page or redirect, mixed content, an insecure form action, or a browser policy issue.
Mixed content is only one possibility.
The decision to make
Why the warning matters
A certificate proves only that a valid TLS connection exists for the covered host. It does not fix HTTP links, mixed content, insecure forms, or incorrect redirects.
Visitors lose confidence
Many people do not investigate the technical details. They see a warning or broken feature and may leave the page.
Technical quality suffers
HTTPS is a baseline for secure delivery, not a guarantee of rankings or overall quality. A half-finished migration can break pages, tracking, forms, and crawl paths.
Trust erodes
Even when visitors do not understand the exact issue, a browser warning or broken interaction makes the site feel unreliable.
What HTTPS is meant to provide
The certificate is only part of the job. The whole page, its resources, its redirects, and its important actions must work through the secure connection.
Encryption
Data between visitors and the website is protected from eavesdropping when TLS is configured correctly.
Data integrity
Data should not be modified during transfer without detection.
Authentication
Visitors should connect to the intended host, with a certificate the browser can validate.
Check every resource after the move
After an HTTP-to-HTTPS move, temporary ranking and crawl changes are possible while Google recrawls the site. First make the secure version complete and reachable.
Images
Scripts and embeds
Content references
Database paths
Remaining resources
One insecure resource can break the secure indication for a page, while a certificate or redirect problem can block the page before mixed-content checks matter.
Fix broad paths, then inspect what remains
Mixed content often comes from a small number of old references, but certificate and redirect faults need separate checks. Start with broad verification, then inspect affected pages individually.
Common causes
- Old image paths;
- insecure scripts or plugins;
- hardcoded content links;
Fix paths
- Search and replace with a verified backup;
- browser and crawl inspection;
- technical help when needed.
Repair and verify the migration
Use broad cleanup first, then inspect anything that remains. For an HTTP-to-HTTPS move, expect recrawl and ranking fluctuation; the time depends on URL count, server capacity, and redirect quality.
Update references
Inspect the browser
Review dependencies
Fix hardcoded paths
Get help when needed
Submit the sitemap
The fix is systematic diagnosis, cleanup, and verification—not guessing.
Frequently asked questions
Why does my site still show Not Secure after HTTPS?
Common causes include an invalid or mismatched certificate, an HTTP page or redirect, mixed content, insecure forms, plugin calls, or hardcoded old references.
How do I find mixed content on a WordPress site?
Start with a verified backup and database search for old site references, then use browser developer tools and a crawl to identify remaining insecure resources and redirect errors.
Will the warning disappear on its own?
No. If it is caused by certificate, redirect, mixed-content, or incomplete migration work, it remains until the cause is fixed and the page loads securely.
A half-finished HTTPS migration is not enough
The certificate is not the finish line. The page, resources, links, forms, plugins, redirects, canonical signals, and sitemap all need to support the secure version.