
Cloudflare cache control
MCP Abilities – Cloudflare: find the stale copy before you purge
You have corrected a page, but a visitor still sees yesterday’s version. Cloudflare may hold a separate copy. Use this WordPress MCP add-on to inspect the public response, choose what to clear and check the page again.
One page can have several cached copies
A WordPress site updates a workshop’s start time, but visitors still see the old time. First check that the saved page is correct. Then distinguish the WordPress server’s cache, Cloudflare’s edge cache and the visitor’s browser cache.
Clearing Cloudflare removes its cached objects. It does not correct unsaved content or clear a visitor’s browser cache. If the origin still serves an old copy, Cloudflare can fetch that same old copy again.
The URL probe reports headers such as CF-Cache-Status, Age and Cache-Control. It does not compare the page text for you. Read the actual response as well; a cache status alone cannot prove the time is correct.
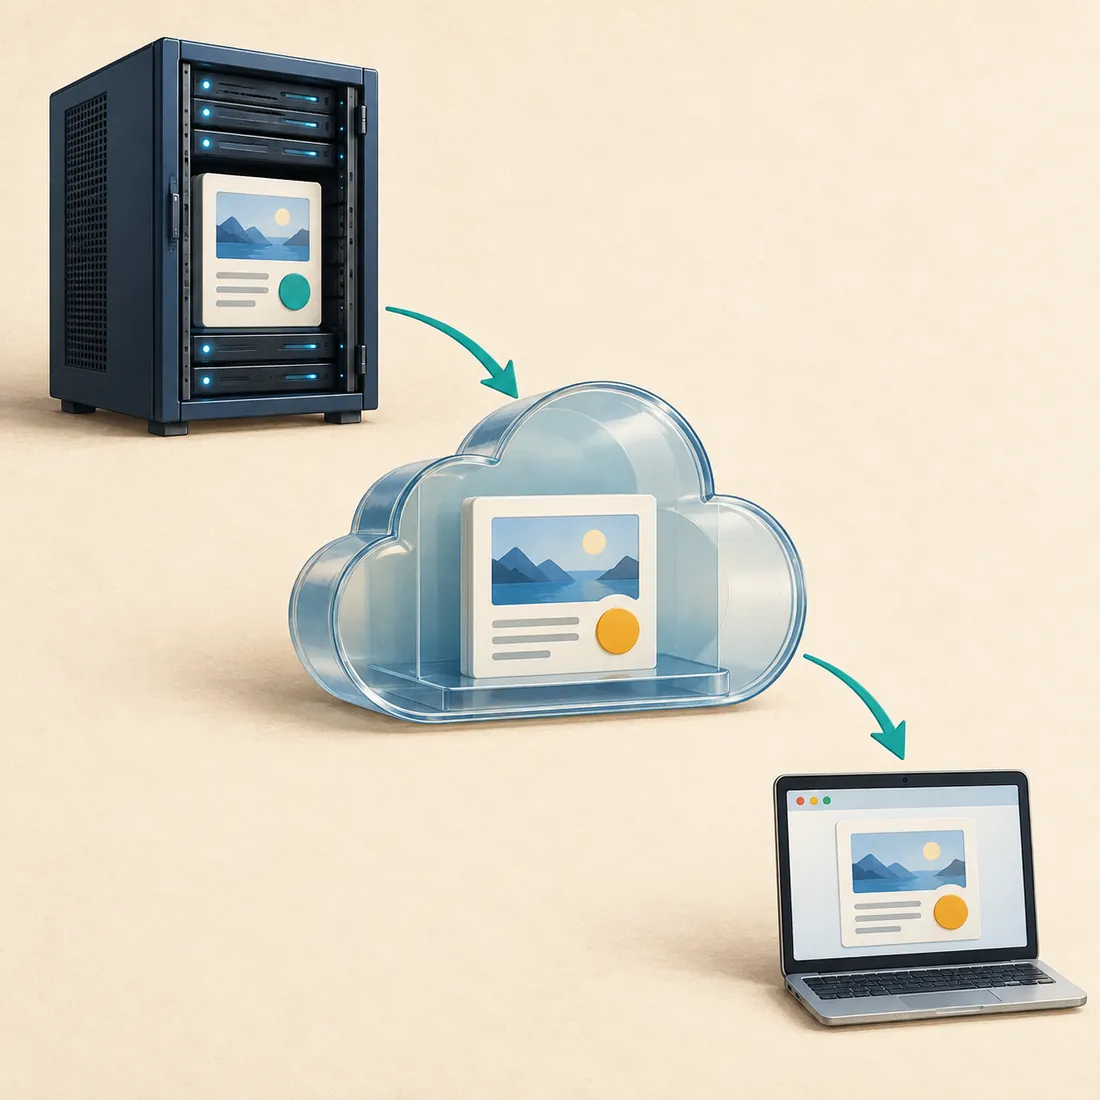
The teal-marked origin copy has changed; the amber-marked edge and browser copies are older. Each layer needs its own check.
A page purge can reach beyond one address
The add-on converts extensionless or .html page URLs without a query string into prefix purges. Asset URLs and URLs with query strings stay exact URL purges. The result lists the automatic prefix conversions.
A prefix such as example.com/classes/ also clears cached resources beneath that path. It is a branch of the site, not one file. Check the hostname, language path and trailing slash before choosing it.
Hosts, cache tags and whole-zone purges cover broader groups. Cloudflare supports these purge methods across its plans, with account limits. Custom cache keys may need headers that this add-on’s string-only file input cannot supply; choose a suitable supported scope.
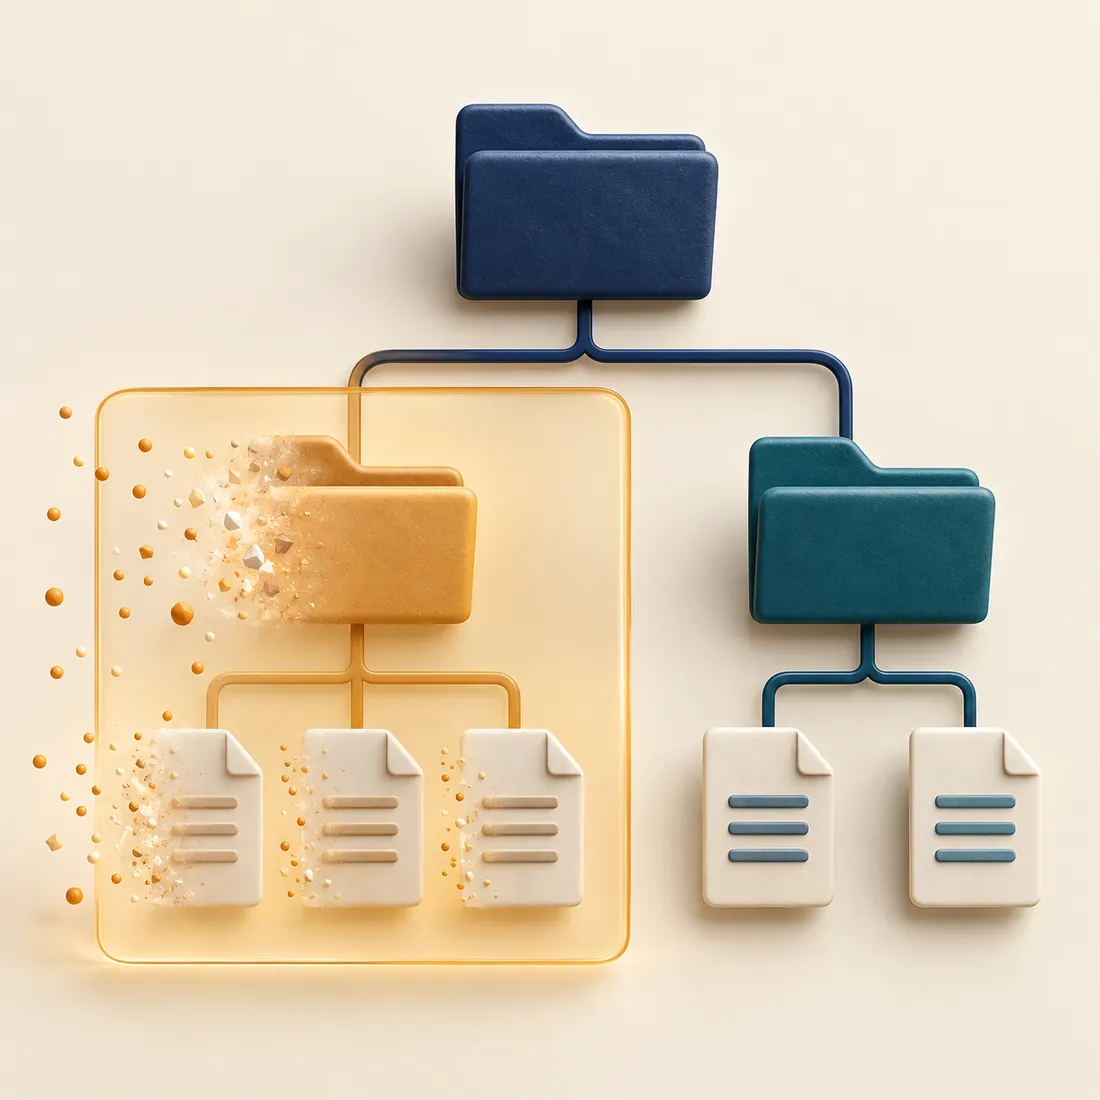
The highlighted branch is the purge scope. Resources below it are included; another branch is outside it.
Inspect, target, clear and verify
1. Confirm the source and zone
Check the saved WordPress content and the exact public URL. Read the connected Cloudflare zone before making a change. An authenticated connection to the wrong zone is still the wrong target.
2. Read the response
Inspect cache settings, rules and the affected URL’s headers. The probe handles at most 20 URLs and repeats each request twice by default. Inspect each attempt and its HTTP status; the outer success value only means the probe finished.
3. Choose the smallest suitable scope
For a targeted purge, explicitly set purge_everything: false and supply checked URLs or prefixes. Review the reported operations, including any completed operations when a later request fails.
4. Check what visitors receive
Request the public page again and verify the changed text or image. A successful Cloudflare purge confirms the request was accepted, not that the origin supplied the correct page. Check browser and local caching separately if the old version remains.
Cache settings need a separate decision
Development Mode temporarily bypasses Cloudflare caching; it does not delete cached files. Cloudflare normally turns it off after three hours. Read its state before changing it, and use a purge when the goal is to remove a stored copy.
The HTML cache-rule action previews its change by default. Its rule targets the selected host and excludes several standard WordPress paths and cookies. It can override the origin’s cache instructions, so previewing the rule is not proof that private pages are safe.
Review custom login, account, checkout and personalised routes before enabling HTML caching. Custom exclusions cover the selected path and its descendants. Inspect the generated expression and test the actual routes and cookies before applying the rule.
The add-on also attempts a purge of the public host’s root prefix after a completed plugin install or update. Account for this automatic behaviour when planning changes; it is broader than clearing one page.
Connect the right WordPress site and Cloudflare zone
The declared minimums are WordPress 6.9 and PHP 8.0. WordPress 6.9 includes the Abilities API. Use a maintained PHP version, an authenticated MCP Adapter connection and a WordPress account with permission to manage site options.
Cloudflare API access needs an appropriate token or key for the intended zone and actions. The official Cloudflare for WordPress plugin can supply credentials; supported WordPress constants are another option.
The credential-configuration action requires the official plugin and exact confirmation. It validates zone access before storing settings without returning the credential. This does not prove the token has every cache or rules permission. Confirm required actions appear in MCP discovery.
For provider behaviour and current limits, see Cloudflare’s purge documentation, Development Mode guide and cache-rule settings.
Start with the page that looks out of date
Install the add-on, confirm the connected zone and inspect the affected URL. Choose a purge scope from the evidence, then verify the page that visitors actually receive.